ls -la ~/writeups
~/writeups/ai-adoption-outran-the-threat-model.md
Sep 27, 2026 · 9 min read
AI arrived in most organizations as diffusion, not deployment — nobody signed off, everybody pasted. A working review of what that adoption actually looks like, the risk classes it carries, and what the next few years plausibly hold. Opinion and observation, not a sourced incident piece.
~/writeups/how-breach-numbers-get-inflated.md
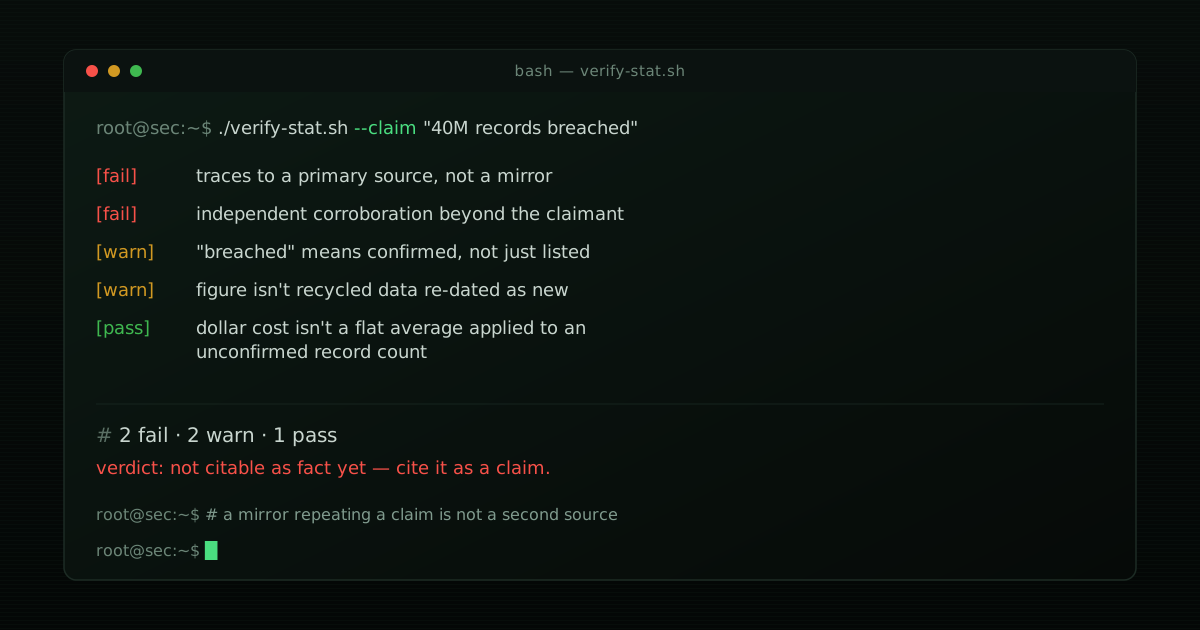
Sep 18, 2026 · 6 min read
"40 million records breached" is usually a claim wearing the costume of a fact. Five ways breach statistics inflate on the way to a headline, and a verification checklist for catching it before you cite one.
~/writeups/the-bot-that-refused-to-start-reading-telegrams-errors-li.md
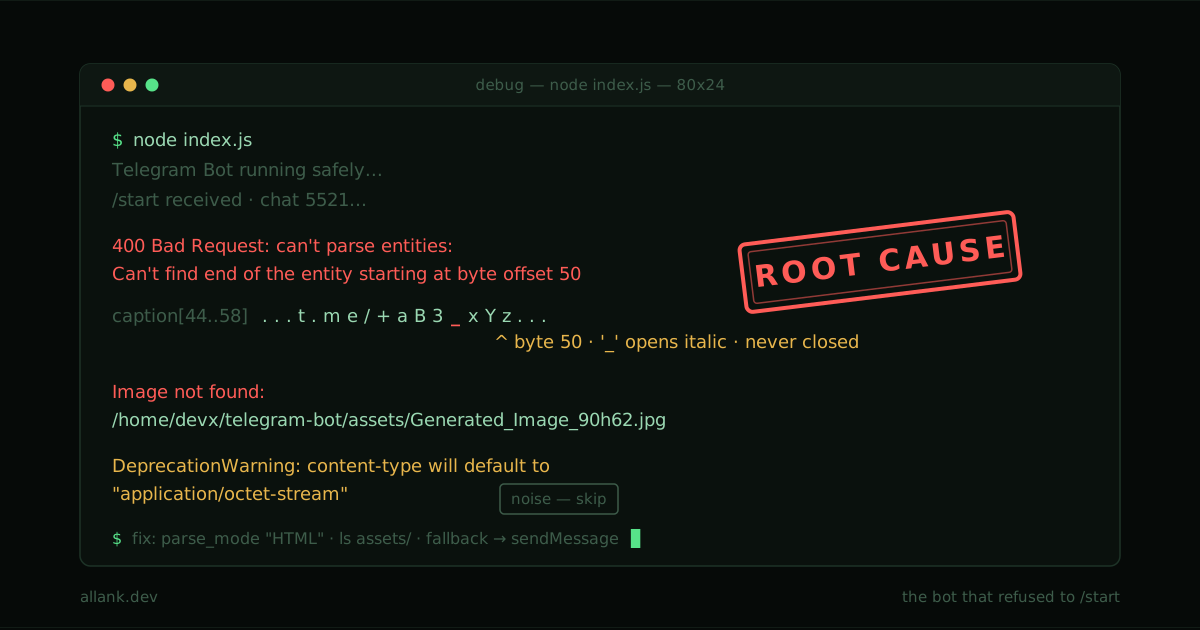
Aug 31, 2026 · 7 min read
A Node.js Telegram bot that should have sent one image, one caption, and three buttons instead produced a parse failure, a missing file, and a deprecation warning — all at once. Untangling which error mattered, which was a red herring, and how to design the handler so none of them crash the process.
~/writeups/the-gentlemen-claim-glassdoor.md
Aug 31, 2026 · 9 min read
On 28 August 2026, the Gentlemen ransomware operation listed Glassdoor on its data leak site — weeks after the platform's legal merger into Indeed. The claim is unverified, no intrusion vector is public, and the company has said nothing. What is known, what is inferred, and why this target is different from the usual victim listing.
~/writeups/how-you-dox-yourself.md
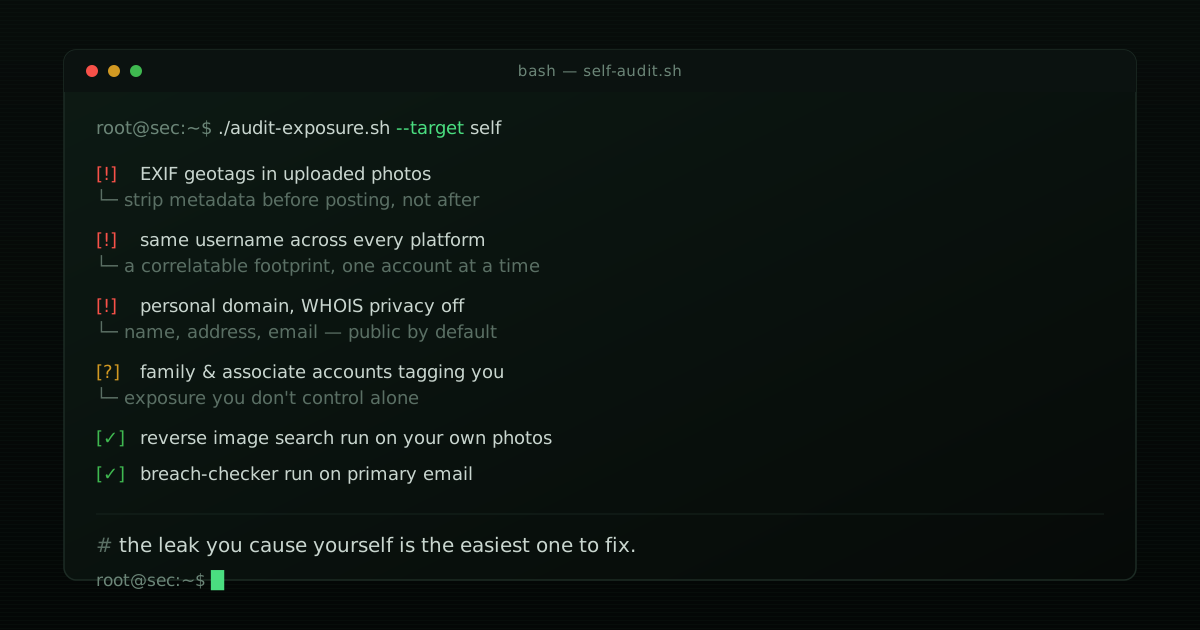
Aug 29, 2026 · 7 min read
Doxing rarely starts with a hacker. It starts with EXIF data, a reused username, an unredacted WHOIS record, or a family account — the everyday habits that build a correlatable profile of you, and how to audit and close them.
~/writeups/splitting-large-csv-files-in-wsl-when-the-tools-fight-back.md
Aug 24, 2026 · 7 min read
Tail throwing Input/output error on a multi-gigabyte CSV in WSL is not a tool failure — it's a diagnosis. Here's what the error actually means, how to verify the root cause, and three paths to clean 100k-row chunks Excel can open.
~/writeups/looking-isnt-neutral-the-hazards-of-dark-web-research-and.md
Aug 19, 2026 · 10 min read
The real risks of dark web research — what you may find, the legal exposure that doesn't hinge on intent, jurisdictional variation, and a harm-reduction posture. Not legal advice.
~/writeups/finding-the-real-video-url.md
Aug 6, 2026 · 8 min read
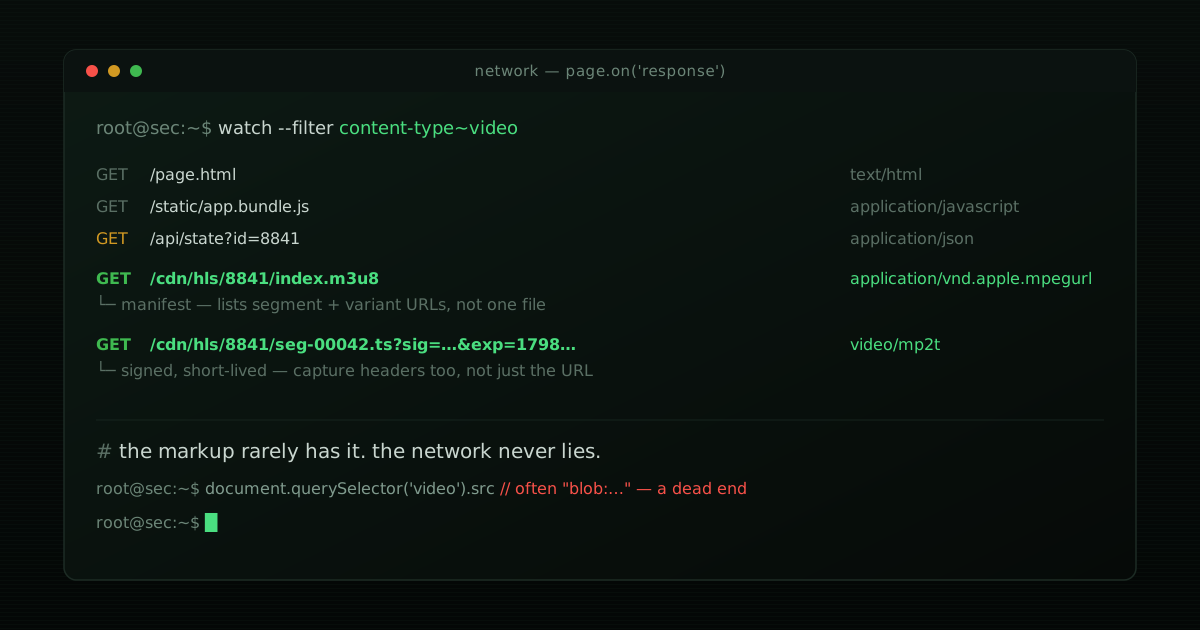
The <video> tag and page source rarely have the answer on modern, JS-rendered pages. A general, platform-agnostic approach to locating the actual media URL — network capture, embedded state JSON, and the two gotchas (blob: URLs, signed links) that break naive approaches.
~/writeups/ifmis-bashe-claim-and-the-discipline-of-saying-only-whats.md
Jul 16, 2026 · 9 min read
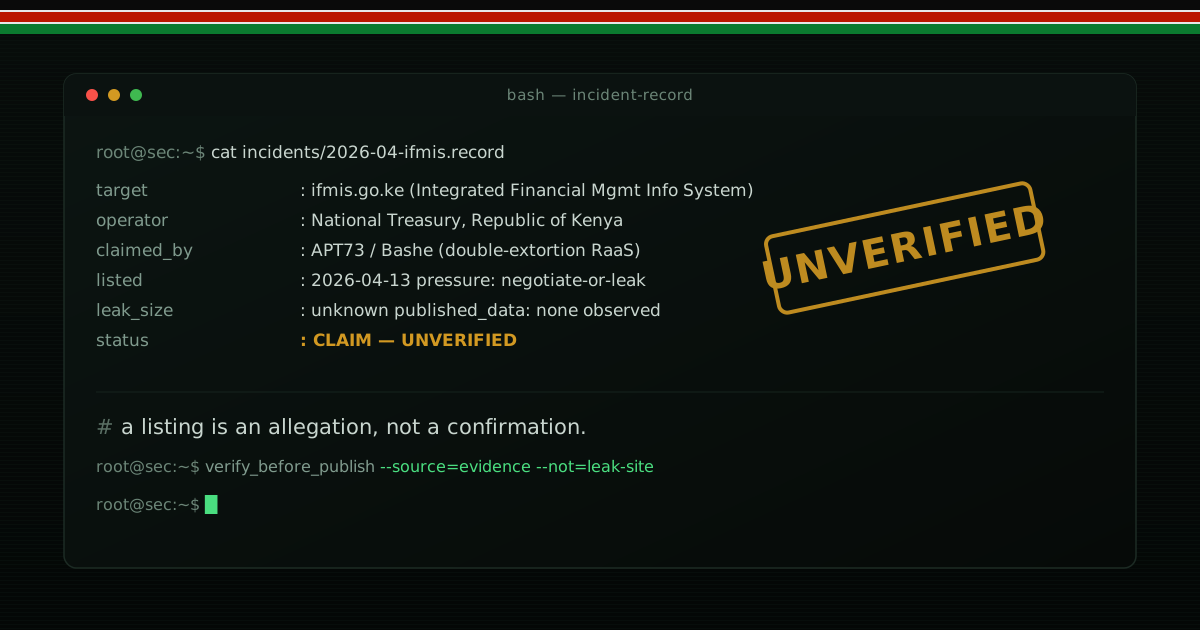
In April 2026 the group APT73/Bashe listed Kenya's IFMIS on its leak site. This is what can actually be verified, what can't, how Kenya's response machinery works, and why the responsible telling stays inside the Data Protection Act.
~/writeups/refactoring-in-the-dark-esdges-of-the-web-hunters-international-world-leaks-and-the-sectors-that-pay-for-it.md
Jul 4, 2026 · 10 min read
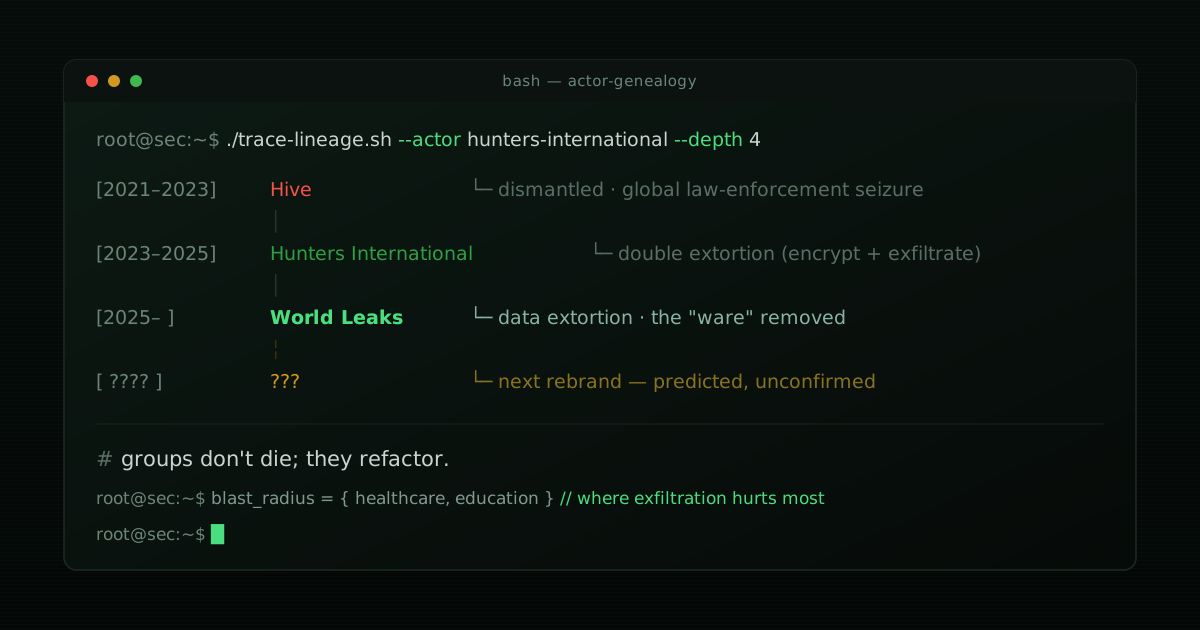
Tracing the Hive → Hunters International → World Leaks lineage, the encryption-less pivot, and why healthcare and education absorb the damage — with defanged sources and confidence-rated attribution.
~/writeups/welcome-to-the-terminal.md
May 2, 2026 · 3 min read
What this blog is for, what it covers, and the ground rules it operates under.